



Recovery objectives
DATABASEstorage2.4 TBqueries/s1,284connections184
ENVIRONMENTSactive3


Document how much data loss and interruption the workload can tolerate. Translate those objectives into testable recovery checks.
Identify the source, data owner, retention policy and authorized restore destination. A policy becomes operational only when the corresponding connector is released.
A completed copy is not a successful recovery. Validate identity, data integrity, dependencies and application behavior in an isolated drill.
Record the policy revision, approval and measured outcome. Separate a planned capability from a verified recovery result.
Assign responsibility for the incident, recovery approval and service validation. Keep rollback and communication requirements in the plan.
Not measured

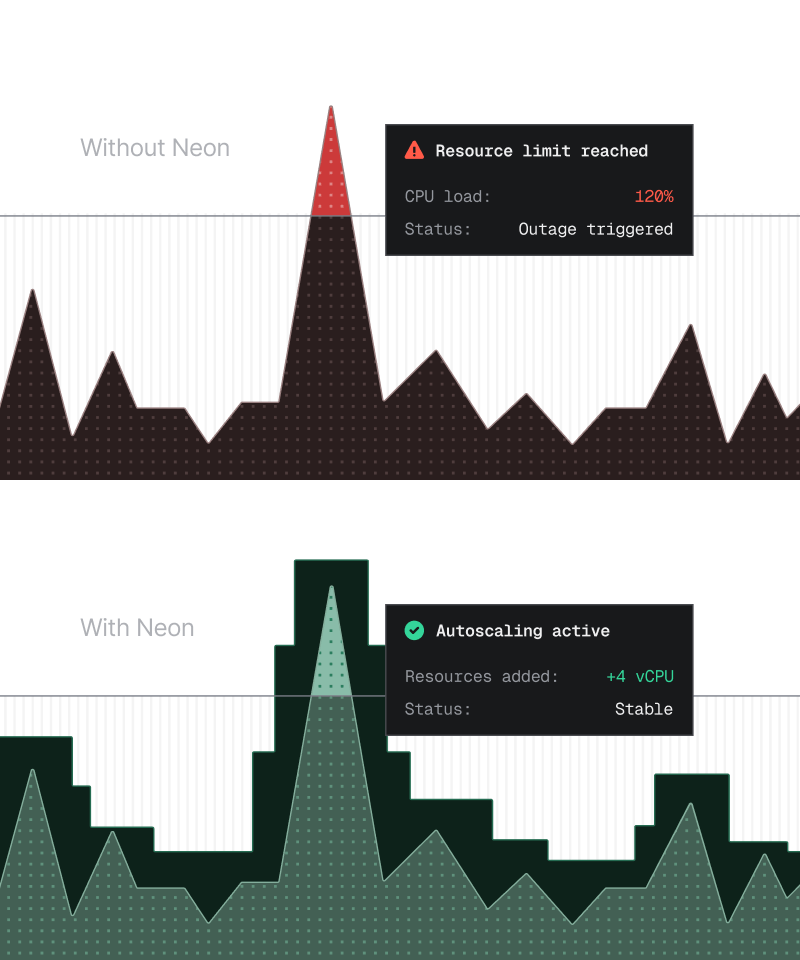
Vinexelprotect autoscaling

Dataset load

Fixed-resource provisioned
Record the policy revision, approval and measured outcome. Separate a planned capability from a verified recovery result.
Assign responsibility for the incident, recovery approval and service validation. Keep rollback and communication requirements in the plan.
Recovery performance, durability and availability need representative tests and applicable contracts. Reference artwork and diagrams do not establish a guarantee.
Document how much data loss and interruption the workload can tolerate. Translate those objectives into testable recovery checks.
Identify the source, data owner, retention policy and authorized restore destination. A policy becomes operational only when the corresponding connector is released.
A completed copy is not a successful recovery. Validate identity, data integrity, dependencies and application behavior in an isolated drill.
Record the policy revision, approval and measured outcome. Separate a planned capability from a verified recovery result.
# Planning example — no product CLI has been released
asset: application-example
owner: workload-owner
environment: staging
action: review-onlyAssign responsibility for the incident, recovery approval and service validation. Keep rollback and communication requirements in the plan.
Recovery performance, durability and availability need representative tests and applicable contracts. Reference artwork and diagrams do not establish a guarantee.
Document how much data loss and interruption the workload can tolerate. Translate those objectives into testable recovery checks.connector_not_released
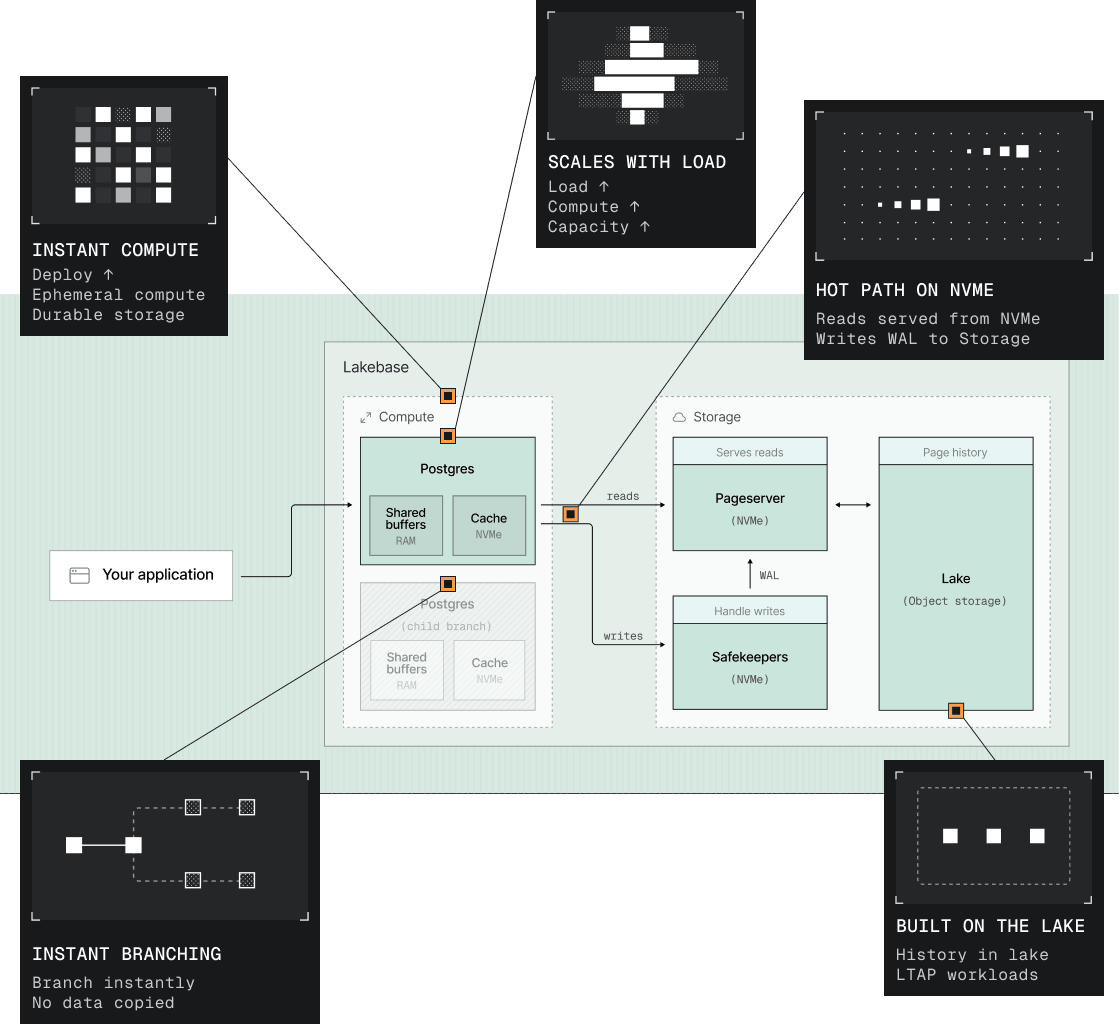
Illustrative product and workflow reference
Identify the source, data owner, retention policy and authorized restore destination. A policy becomes operational only when the corresponding connector is released. Existing account forms use IAM Central; the current console uses Elpixe Dashkit.
Last updated on
Record the policy revision, approval and measured outcome. Separate a planned capability from a verified recovery result.
Assign responsibility for the incident, recovery approval and service validation. Keep rollback and communication requirements in the plan.
A useful workflow makes the owner, authorization, evidence and validation visible. Illustrative product principle; no customer endorsement is claimed.
Recovery performance, durability and availability need representative tests and applicable contracts. Reference artwork and diagrams do not establish a guarantee.
Only published languages are listed. Theme preference is stored locally in this browser.