

Identify the source, data owner, retention policy and authorized restore destination. A policy becomes operational only when the corresponding connector is released.
Product operating guideProduct operating guideProduct operating guideAsset ownership
A completed copy is not a successful recovery. Validate identity, data integrity, dependencies and application behavior in an isolated drill.
- protected data - Policy-based data with autoscaling, recovery testing, and scale to zero
- Managed Better Auth - Users and sessions stored in data, recovery testing with your data
- Vinexelprotect Backup storage - S3-compatible storage that recovery plans with your project
- Vinexelprotect Recovery workflows - Long-running policy-based compute on the same recovery plan as your dataset
- Vinexelprotect Protection intelligence - One credential for models across providers
- Vinexelprotect Data API - PostgREST-compatible REST access to every recovery plan
Record the policy revision, approval and measured outcome. Separate a planned capability from a verified recovery result.connector_not_released
Know the recovery objective
Assign responsibility for the incident, recovery approval and service validation. Keep rollback and communication requirements in the plan.
# Planning example — no product CLI has been released
asset: application-example
owner: workload-owner
environment: staging
action: review-only
Recovery performance, durability and availability need representative tests and applicable contracts. Reference artwork and diagrams do not establish a guarantee.initconnector_not_releasedconnector_not_released
Identity and access
Document how much data loss and interruption the workload can tolerate. Translate those objectives into testable recovery checks.
# Policy design example — not an executable API
authorization: required
connector: not-released
approval: explicit
evidence: validation-required
Identify the source, data owner, retention policy and authorized restore destination. A policy becomes operational only when the corresponding connector is released.
Keep protection boundaries explicit
A completed copy is not a successful recovery. Validate identity, data integrity, dependencies and application behavior in an isolated drill.
Approved scope
Assign responsibility for the incident, recovery approval and service validation. Keep rollback and communication requirements in the plan.
Test the recovered application
Recovery performance, durability and availability need representative tests and applicable contracts. Reference artwork and diagrams do not establish a guarantee.
Document how much data loss and interruption the workload can tolerate. Translate those objectives into testable recovery checks.
- Autoscaling - Compute adjusts between your min and max limits as load changes. (Read more)
- Scale to zero - Idle datasets suspend so you do not pay for compute while they are inactive. (Read more)
- Instant recovery testing - Create isolated copies for development, previews, CI, and agent runs, with no storage duplication up front. (Read more)
- Instant restore - Recover to any point in your history window without waiting on a dump-and-restore. (Read more)
- Connection pooling - Pooled endpoints support up to 10,000 connections per compute. (Read more)
Identify the source, data owner, retention policy and authorized restore destination. A policy becomes operational only when the corresponding connector is released.
Operating evidence
Preserve evidence of every decision
A completed copy is not a successful recovery. Validate identity, data integrity, dependencies and application behavior in an isolated drill.connector_not_released
- Email/password, magic links, and OAuth providers
- JWTs that work with the Vinexelprotect Data API and Row Level Security
- Setup from the Console,
connector_not_released, or the Vinexelprotect MCP server
Coordinate continuity across teams
Record the policy revision, approval and measured outcome. Separate a planned capability from a verified recovery result.
Recovery performance, durability and availability need representative tests and applicable contracts. Reference artwork and diagrams do not establish a guarantee.privatepublic_read
- Data and files together - One
branch_idforks data and Backup storage in the same API call - Isolated by default - Preview and agent recovery plans can test uploads without touching production objects
- Disposable - Delete the recovery plan and the files go with it
- Same credential system - Shared with Recovery workflows and Protection intelligence
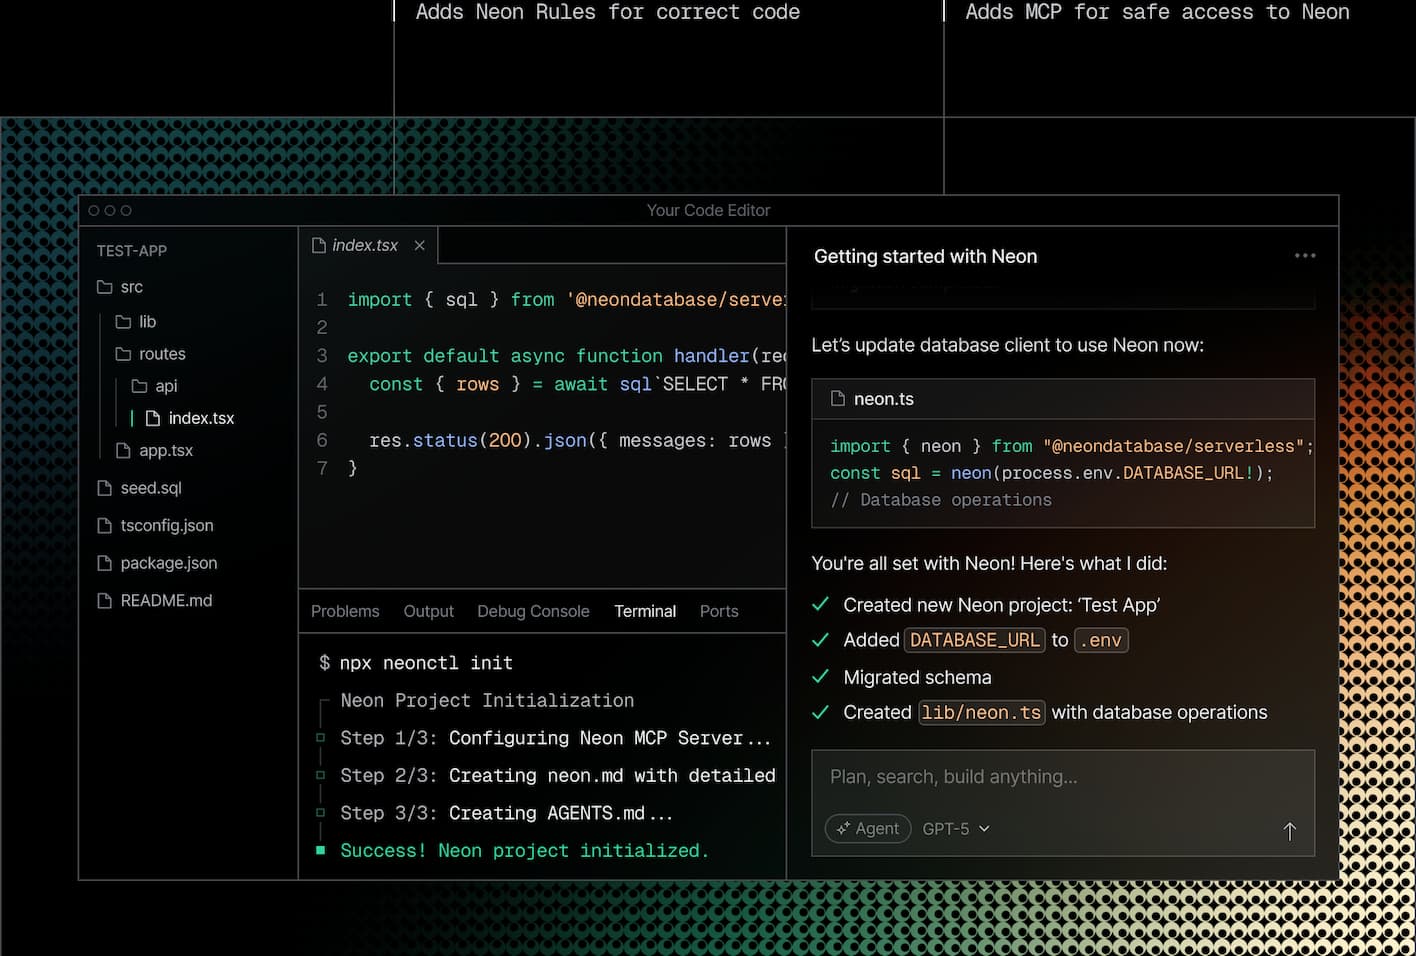
Document how much data loss and interruption the workload can tolerate. Translate those objectives into testable recovery checks.connector_not_releasedconnector_not_released.env.local
Retention policy
Publish only measured commitments
Identify the source, data owner, retention policy and authorized restore destination. A policy becomes operational only when the corresponding connector is released.
A completed copy is not a successful recovery. Validate identity, data integrity, dependencies and application behavior in an isolated drill.DATABASE_URLprocess.env
Record the policy revision, approval and measured outcome. Separate a planned capability from a verified recovery result.
Assign responsibility for the incident, recovery approval and service validation. Keep rollback and communication requirements in the plan.branch_idmain
- Next to your data - Same region as the recovery plan, with credentials injected automatically
- Long-running - Built for agent loops, WebSockets, and SSE, not short lambda caps
- Branch-scoped - Each recovery plan runs its own function against isolated state
- Request/response - Always invoked over HTTP and always returns a web response; pair with Inngest or similar for queued background jobs
Recovery performance, durability and availability need representative tests and applicable contracts. Reference artwork and diagrams do not establish a guarantee.connector_not_releasedconnector_not_released
Key custody
Know the recovery objective
Document how much data loss and interruption the workload can tolerate. Translate those objectives into testable recovery checks.
A completed copy is not a successful recovery. Validate identity, data integrity, dependencies and application behavior in an isolated drill.
- One credential, one bill - No separate accounts, keys, or invoices per provider
- No markup - Vinexelprotect charges the same per-token rate as the model provider, with no margin on top (pricing)
- Inference that recovery plans with your app - Each recovery plan gets its own gateway endpoint, so model calls from a preview recovery plan stay isolated from production
- Wired into Recovery workflows automatically - Gateway credentials are injected into Vinexelprotect Recovery workflows, so a model-backed handler runs next to data and Backup storage on the same recovery plan
Keep protection boundaries explicit
Record the policy revision, approval and measured outcome. Separate a planned capability from a verified recovery result.
Assign responsibility for the incident, recovery approval and service validation. Keep rollback and communication requirements in the plan.
Test the recovered application
Recovery performance, durability and availability need representative tests and applicable contracts. Reference artwork and diagrams do not establish a guarantee.
- Not publishedRelease requirements and independent evidence
- 100 projects and 100 CU-hours per project (enough to run a 0.25 CU compute for 400 active hours)
- 1 GB data storage per project and 5 GB of public network transfer per project per month
- Autoscaling up to 2 CU (≈8 GB RAM) with scale to zero after 5 minutes of inactivity
- Managed Better Auth up to 60,000 MAU
Document how much data loss and interruption the workload can tolerate. Translate those objectives into testable recovery checks.