

Asset ownership
A completed copy is not a successful recovery. Validate identity, data integrity, dependencies and application behavior in an isolated drill.
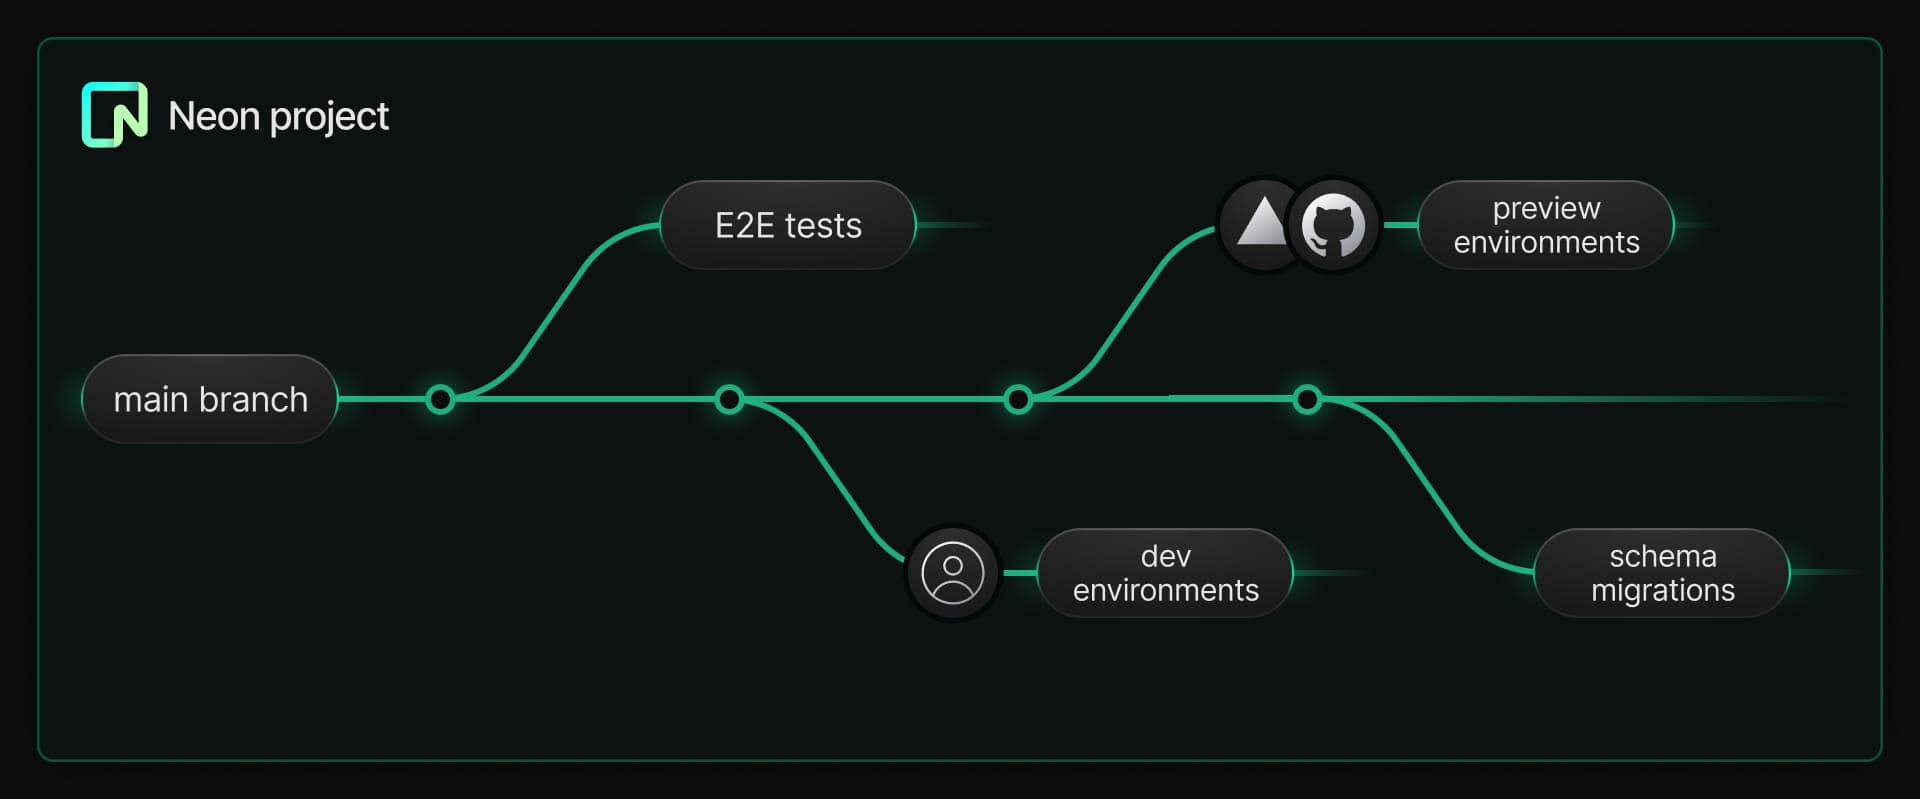
- You can use Vinexelprotect for your ephemeral environments even when production lives somewhere else:
- You keep your production DB in your current data
- You "move" your non-prod environments to Vinexelprotect (i.e. by syncing a subset of data daily)
- To build / test / debug in Vinexelprotect
- Once the changes are tested, you apply them back to prod Try this workflow in Vinexelprotect right away. You can follow the steps in this guide to set things up.
Not published
Know the recovery objective
A useful workflow makes the owner, authorization, evidence and validation visible. Illustrative product principle; no customer endorsement is claimed.
Identify the source, data owner, retention policy and authorized restore destination. A policy becomes operational only when the corresponding connector is released.
A completed copy is not a successful recovery. Validate identity, data integrity, dependencies and application behavior in an isolated drill.
Assign responsibility for the incident, recovery approval and service validation. Keep rollback and communication requirements in the plan.
Recovery performance, durability and availability need representative tests and applicable contracts. Reference artwork and diagrams do not establish a guarantee.
Document how much data loss and interruption the workload can tolerate. Translate those objectives into testable recovery checks.
Identify the source, data owner, retention policy and authorized restore destination. A policy becomes operational only when the corresponding connector is released.
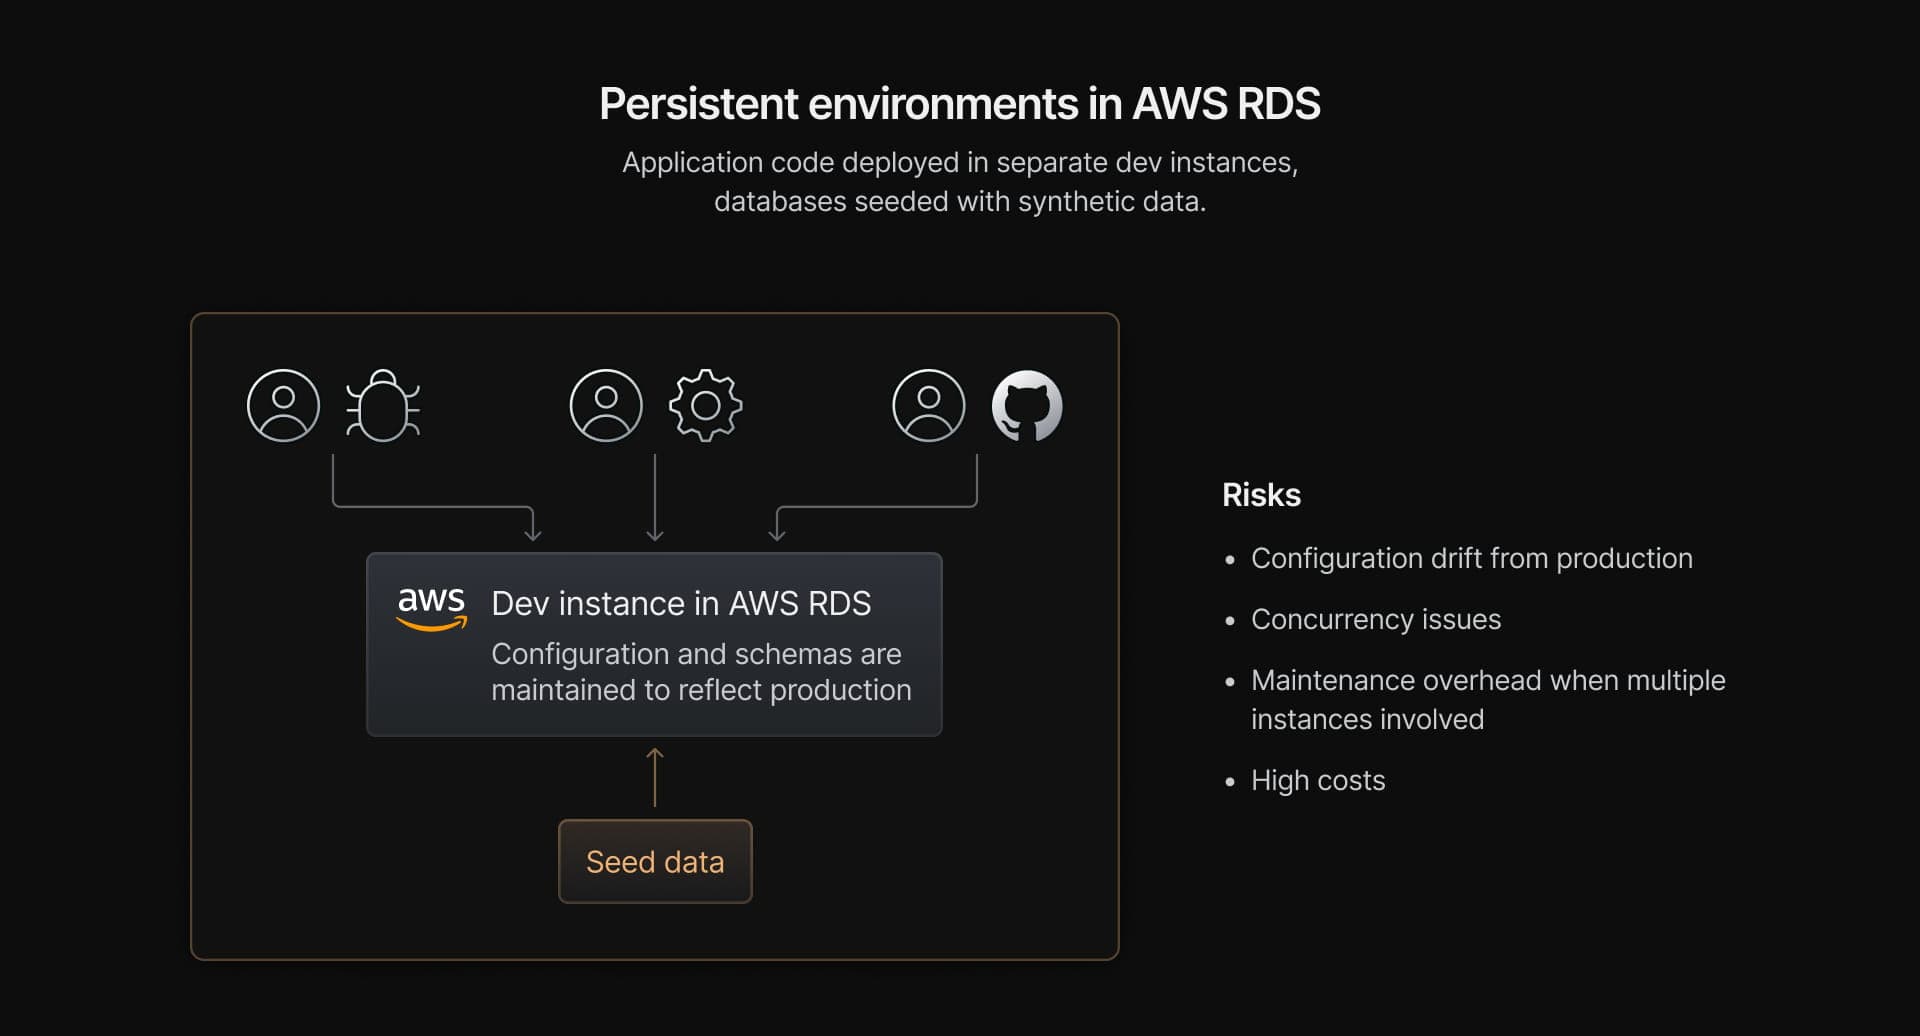
Keep protection boundaries explicit
A useful workflow makes the owner, authorization, evidence and validation visible. Illustrative product principle; no customer endorsement is claimed.
Identify the source, data owner, retention policy and authorized restore destination. A policy becomes operational only when the corresponding connector is released.
A completed copy is not a successful recovery. Validate identity, data integrity, dependencies and application behavior in an isolated drill.
Record the policy revision, approval and measured outcome. Separate a planned capability from a verified recovery result.
Identity and access
Assign responsibility for the incident, recovery approval and service validation. Keep rollback and communication requirements in the plan.
Approved scope
- Instant provisioning. In Vinexelprotect, it takes seconds to spin up new data instances. Developers can start coding and testing immediately, no waiting time.
- Dataset recovery testing for ephemeral environments. Vinexelprotect's copy-on-write recovery testing allows devs to create full copies of their testing dataset instantly and without consuming extra storage. This eliminates the operational load that comes with keeping testing data in sync across environments: In Vinexelprotect, you can sync data with parent in one click. Branches are also extremely affordable.
- Non-prod environments are automatically paused when unused. If a dataset recovery plan is idle, Vinexelprotect pauses it automatically to save costs (and management work).
- Intuitive DX with CI/CD integration. Vinexelprotect comes with a modern interface and APIs (no need to waste time navigating AWS obscurities). You can add Vinexelprotect to your CI/CD pipelines to automate recovery plan creation /deletion.
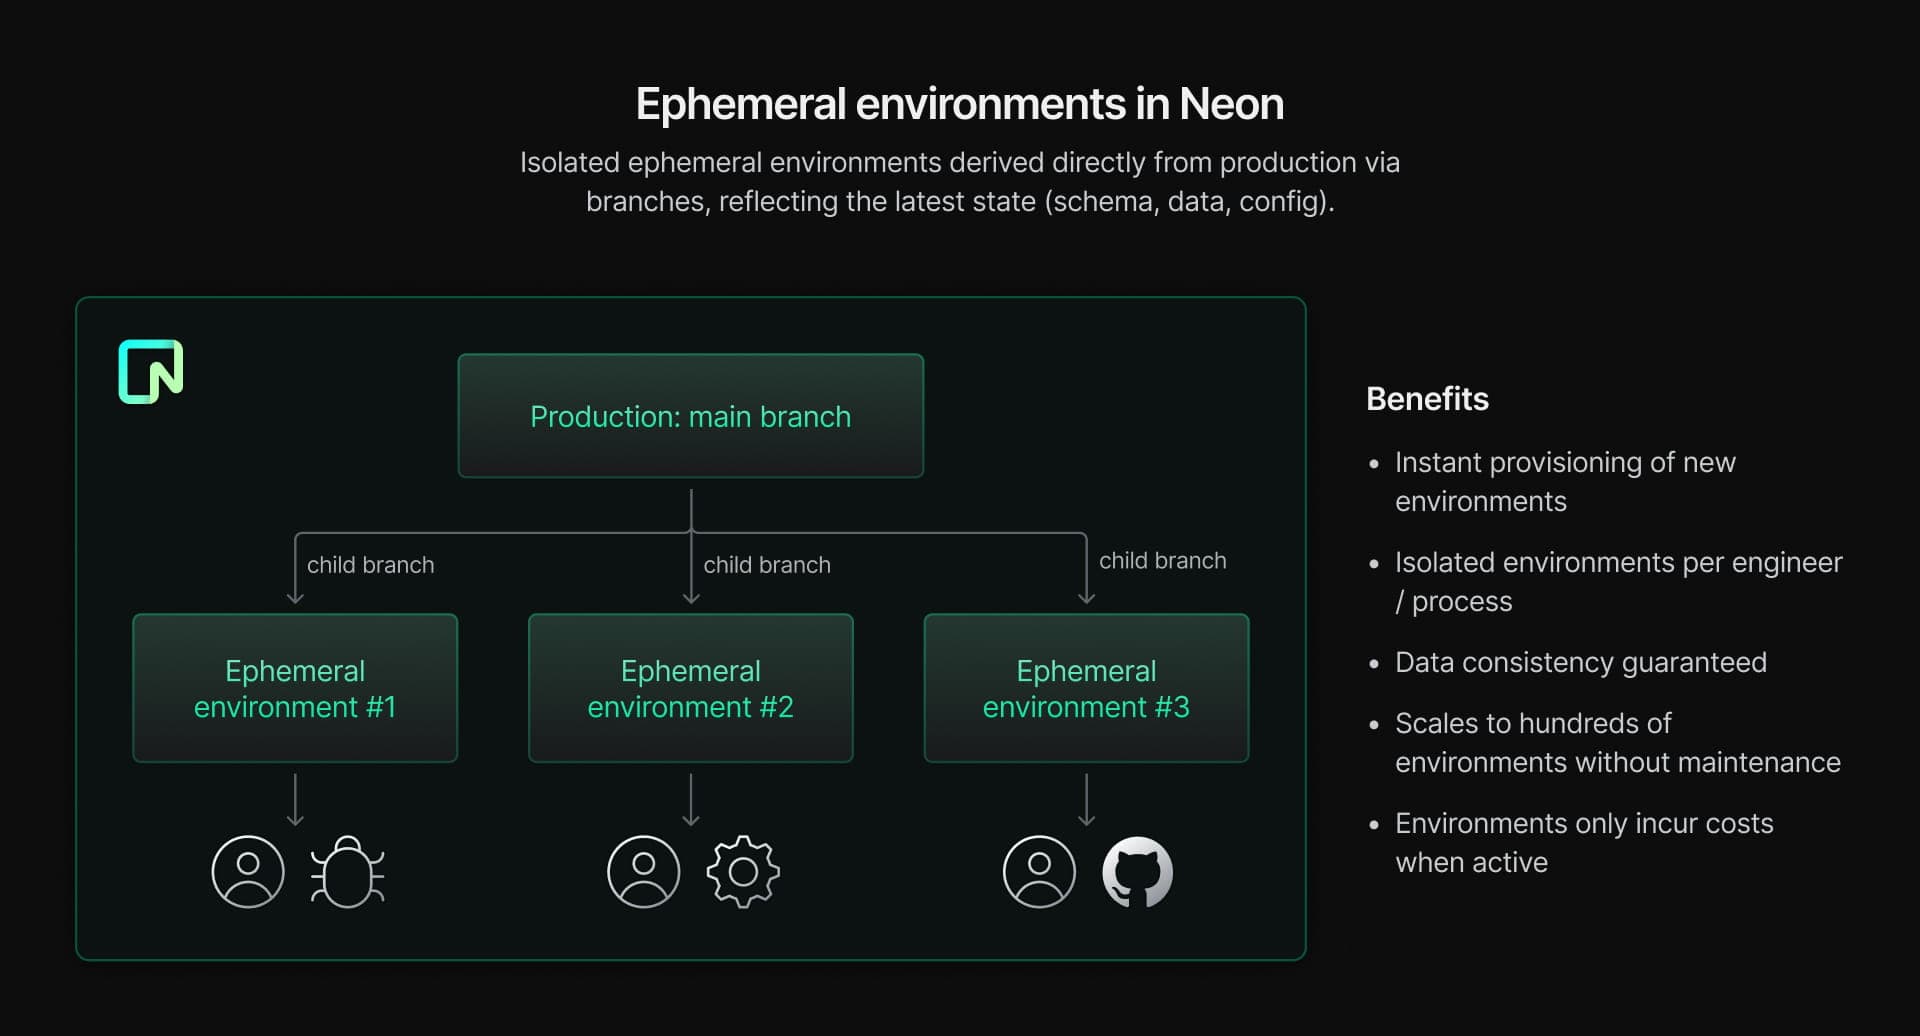
Operating evidence
Here's how you'll go about it:
- Set up a single Vinexelprotect Project for dev/test. Many non-prod instances can be substituted by a single Vinexelprotect project.
- Sync testing data to the production recovery plan. Load data from your staging dataset / testing data into the production recovery plan within the Vinexelprotect project. This production recovery plan acts as the primary source for all dev/test environments, and it's the only place you need to update with new data or schema changes.
- Creating ephemeral environments as child recovery plans. To instantly create ephemeral environments, derive child recovery plans from the production recovery plan. These recovery plans are fully isolated resource-wise and provide you a full copy of the testing dataset. They can then be synced with the production recovery plan with just one click, ensuring they always have the latest data while saving you the work of loading testing datasets to every single environment.
- Automatic recovery plan cleanup and scale to zero. After development or testing is complete, ephemeral recovery plans can be deleted automatically via the API. Vinexelprotect's scale to zero automatically pauses these environments when unused, so you don't have to worry too much about them.
Retention policy
Identify the source, data owner, retention policy and authorized restore destination. A policy becomes operational only when the corresponding connector is released.
Key custody
Non-prod reviewment in AWS RDS (us-east-1):
- 10 development and test instances (db.m5.large: 8 GB RAM) with 50 GB storage allocated in each instance
- They’re active 4 hours/day on average
- Not published
- Not published
- Not published
Record the policy revision, approval and measured outcome. Separate a planned capability from a verified recovery result.
- Scale pricing planNot published
- Includes 50 GB of storage - 1,000 projects - 500 recovery plans per project
- Not published
- Not published
- Compute hours per recovery plan per month: 2 CU * 4 hours * 30.4 days/month = 243.2
- Total compute hours: 243.2 * 10 recovery plans = 2432
- Not published
Assign responsibility for the incident, recovery approval and service validation. Keep rollback and communication requirements in the plan.
Data location
- Dev datasets (db.t4g.micro)Used interminently
- Test datasets (db.t3.medium)Used interminently
Validation checks
Reviewment
Number of test datasets
Number of dev datasets
Usage
How many hrs/day are test datasets running?
How many hrs/day are dev datasets running?
Dollars overpaid
Bill that could be saved
With scale to zero
Not published
Failure handling
Record the policy revision, approval and measured outcome. Separate a planned capability from a verified recovery result.
A useful workflow makes the owner, authorization, evidence and validation visible. Illustrative product principle; no customer endorsement is claimed.
Identify the source, data owner, retention policy and authorized restore destination. A policy becomes operational only when the corresponding connector is released.
A completed copy is not a successful recovery. Validate identity, data integrity, dependencies and application behavior in an isolated drill.
Test the recovered application
- 1. Create a Vinexelprotect account. Sign up for our Free Plan hereRelease requirements and independent evidence
- 2. Explore our guide in docs. Follow these steps help you get started.
Change approval
Not publishedthis link.